Modprobe: Managing Dynamic Kernel Modules, Passing Runtime Subsystem Parameters, and Hardening Driver Security in Production
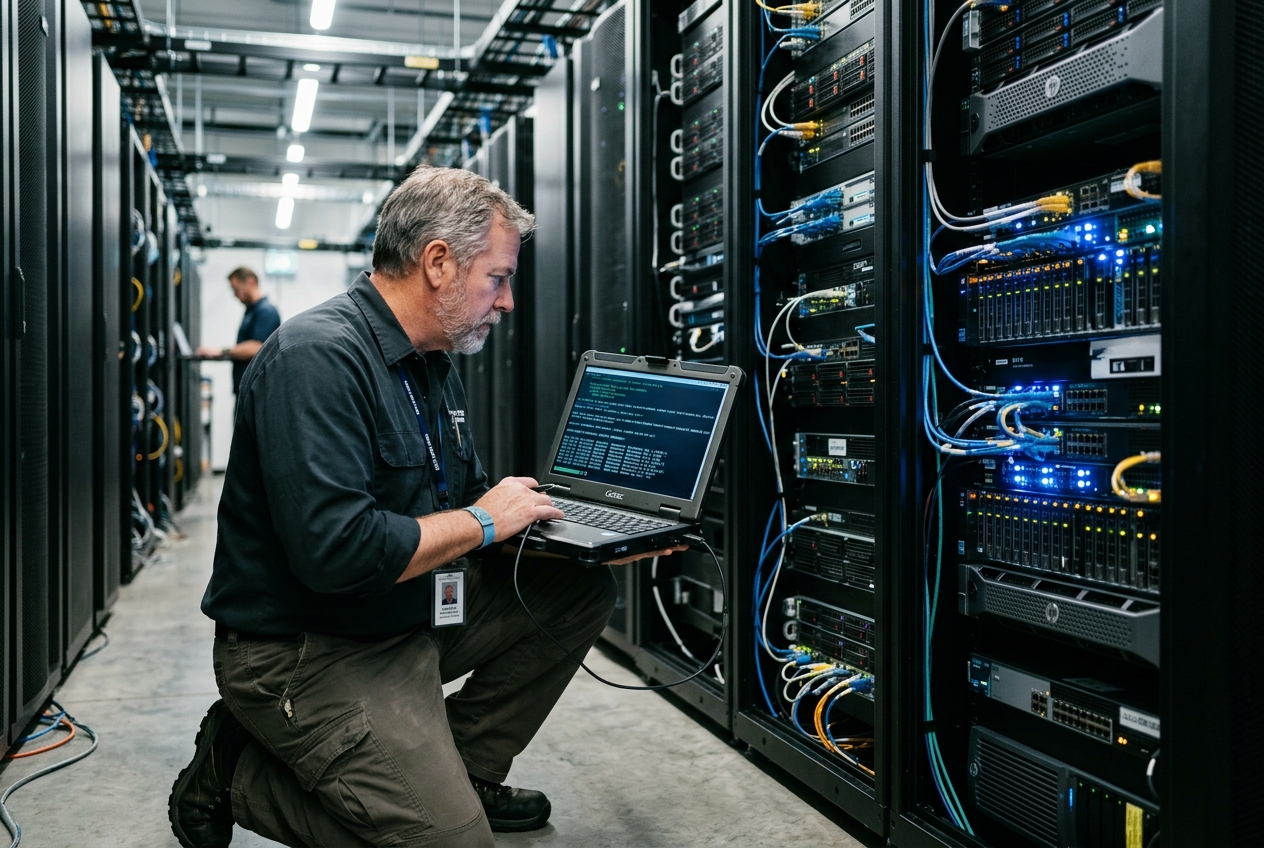
In production environments, you cannot simply press the reset button or schedule a leisurely maintenance window when an automated update mangles a driver or leaves network interfaces misconfigured. You have minutes to dissect the failure, modify how the running operating system interacts with its hardware, and restore service—all without rebooting the machine.
When disaster strikes, the single most valuable command in an engineer's toolkit is a safe dry run using modprobe:
sudo modprobe -nv bonding
This simple command simulates the entire insertion process. It inspects local configuration rules, traces prerequisite dependencies, and prints the exact kernel execution plan without altering a single byte of live system memory.
The Linux operating system runs on a modular architecture. Rather than compiling every conceivable network card, disk controller, and encryption algorithm into a rigid, monolithic binary file that must be recompiled for every hardware tweak, Linux loads and unloads functional components dynamically while the machine is running. These dynamically loaded components are known as loadable kernel modules (LKMs).
The modprobe utility acts as the intelligent conductor for this modular orchestra. Unlike primitive loading tools that attempt to force raw code into memory, modprobe works methodically: it resolves prerequisite software dependencies, applies local parameter rules from system configuration directories, and seamlessly links the driver into live memory without interrupting the rest of the machine.
What It Does in Plain English
Imagine the Linux kernel as an running engine that never stops spinning. When you plug in a new high-speed network adapter or enable a specialized filesystem, the operating system needs the specific instructions required to speak to that hardware.
Instead of shutting down the entire engine to bolt on a new part, the kernel dynamically loads a module—a self-contained block of compiled code that extends the kernel's capabilities on the fly.
Managing these modules manually, however, is fraught with peril. A single storage driver might depend on three separate cryptographic libraries and an asynchronous communication subsystem. If you attempt to load that driver in isolation, the operating system will fail with cryptic errors about missing symbols.
modprobe eliminates this operational friction. When invoked, it consults a pre-indexed map of your system's drivers, identifies every required prerequisite, reads your custom performance settings from /etc/modprobe.d/, and inserts the entire chain in the exact sequence required.
Architectural Foundations: modprobe vs. insmod
To appreciate why modprobe is standard across modern Linux deployments, one must understand how user-space tools interact with kernel space.
The Dichotomy Between Raw and Intelligent Insertion
Linux provides a low-level command named insmod, which is a direct wrapper around kernel system calls such as init_module(2) or finit_module(2). However, insmod requires an exact, absolute file path (such as /lib/modules/6.8.0-40-generic/kernel/drivers/net/bonding/bonding.ko.zst) and possesses zero contextual awareness. If the target module depends on symbols provided by another driver, insmod fails immediately with an unhelpful Unknown symbol in module error in system logs. It also ignores any custom options placed in configuration files.
In contrast, modprobe provides an intelligent management layer:
- Symbol and Dependency Graph Resolution: It consults the binary database
modules.dep.bin, generated automatically bydepmod, locating and inserting all prerequisite modules in strict topological sequence before attempting to insert the target module. - Rule-Driven Parameter Injection: It parses configuration directories (
/etc/modprobe.d/,/run/modprobe.d/, and/usr/lib/modprobe.d/) to apply aliases, performance tuning parameters, blacklists, and pre/post-installation hooks. - Location Abstraction: Modules are referenced simply by their canonical name (such as
bonding), abstracting away complex kernel release directory paths.
Live Kernel Interfaces: /proc/modules and /sys/module/
Once loaded into live memory, two virtual filesystems expose module state:
/proc/modulesfunctions as the real-time textual ledger of all active modules, detailing memory footprints, active instance reference counts, dependent modules, and current state (Live,Loading, orUnloading).- The
/sys/module/directory undersysfsprovides an interactive tree for every loaded module. In particular,/sys/module/<module_name>/parameters/exposes the active runtime parameters, allowing administrators to inspect or modify operational parameters on the fly.
Core Flags & Quick Start
Before troubleshooting complex production scenarios, administrators should master the primary command-line switches that control modprobe:
| Flag | Name | Operational Purpose |
|---|---|---|
-v |
--verbose |
Displays detailed operational output, revealing underlying dependency insertions and parameter injections. |
-r |
--remove |
Unloads the specified module and safely cascades through its unused dependencies, provided their reference counts are zero. |
-n |
--dry-run |
Executes configuration parsing and dependency tree checks without executing the final kernel module insertion system call. |
-c |
--showconfig |
Dumps the consolidated configuration compiled across all /etc/modprobe.d/, /run/modprobe.d/, and /usr/lib/modprobe.d/ paths. |
-d |
--dirname |
Overrides the root directory where /lib/modules/ is located (invaluable during chroot rescues or offline filesystem recovery). |
-a |
--all |
Accepts multiple module names in a single command, resolving and loading each stack sequentially. |
Quick Start Verification
To observe modprobe resolving and inserting a driver with verbose tracking, load the virtual dummy network adapter:
sudo modprobe -v dummy
insmod /lib/modules/6.8.0-40-generic/kernel/drivers/net/dummy.ko.zst
Verify that the kernel has accepted the module and created its control structures in sysfs:
ls -ld /sys/module/dummy
drwxr-xr-x 5 root root 0 Aug 18 02:15 /sys/module/dummy
5 Real-World Production Scenarios
1. Dynamic High-Performance Network Driver Tuning (802.3ad Bonding)
The Scenario
A systems engineer is provisioning a high-throughput storage node connected to dual top-of-rack switches. Two 25GbE network interfaces (ens1f0 and ens1f1) must be aggregated into an IEEE 802.3ad Dynamic Link Aggregation interface (bond0). To ensure balanced traffic distribution across both physical links for database streams, the bonding driver must initialize with Link Aggregation Control Protocol (LACP), 100ms link monitoring (miimon), and Layer 2+3 transmit hashing (xmit_hash_policy=layer2+3).
Configuration File
Rather than passing transient command-line arguments, create a permanent configuration file conforming to modprobe.d(5):
sudo tee /etc/modprobe.d/bonding.conf << 'EOF'
# Production LACP Bonding Configuration for NVMe-over-Fabrics Storage Nodes
alias bond0 bonding
options bonding mode=802.3ad miimon=100 xmit_hash_policy=layer2+3 lacp_rate=fast
EOF
Execution Command
Load the driver with verbose tracking:
sudo modprobe -v bonding
Realistic Terminal Output
insmod /lib/modules/6.8.0-40-generic/kernel/drivers/net/bonding/bonding.ko.zst mode=802.3ad miimon=100 xmit_hash_policy=layer2+3 lacp_rate=fast
Line-by-Line Technical Analysis
insmod /lib/modules/.../bonding.ko.zst:modprobelocated the compressed driver object corresponding to the running kernel release.mode=802.3ad: Instructs the bonding subsystem to negotiate dynamic aggregation via standard LACP control frames (802.3ad / Mode 4).miimon=100: Directs the Media Independent Interface monitor to poll physical carrier health every 100 milliseconds.xmit_hash_policy=layer2+3: Configures the internal hashing algorithm to generate load-balancing keys using both MAC addresses and IP addresses, preventing single-connection bottlenecks across the aggregated links.lacp_rate=fast: Requests LACP control packets from connected switches every 1 second instead of the default 30-second heartbeat.
Parameter Validation via Sysfs
cat /sys/module/bonding/parameters/mode
cat /sys/module/bonding/parameters/xmit_hash_policy
802.3ad 4
layer2+3 1
What the Administrator Does Next
Bind the physical network adapters to the virtual bond interface and activate the link using iproute2:
sudo ip link add name bond0 type bond
sudo ip link set dev ens1f0 down && sudo ip link set dev ens1f0 master bond0
sudo ip link set dev ens1f1 down && sudo ip link set dev ens1f1 master bond0
sudo ip link set dev bond0 up
cat /proc/net/bonding/bond0
2. Kernel Security Hardening & Protocol Blacklisting
The Scenario
To comply with security benchmarks (such as CIS Controls or NIST SP 800-53), a financial server must disable legacy or unneeded network protocols, including Datagram Congestion Control Protocol (dccp) and Stream Control Transmission Protocol (sctp), as well as obsolete filesystems like cramfs.
Standard blacklist directives alone are insufficient because user-space applications requesting a socket (e.g. socket(AF_INET, SOCK_DCCP, 0)) can trigger the kernel's automatic module-loading mechanism (request_module()), bypassing basic blacklists.
Configuration File
Enforce a fail-safe override by redirecting installation requests to /bin/true:
sudo tee /etc/modprobe.d/cis-hardening.conf << 'EOF'
# CIS Benchmark Compliance: Disable vulnerable transport protocols and filesystems
install dccp /bin/true
install sctp /bin/true
install rds /bin/true
install tipc /bin/true
install cramfs /bin/true
install firewire-core /bin/true

# Explicit blacklisting to prevent indirect module graph resolution
blacklist dccp
blacklist sctp
blacklist rds
blacklist tipc
blacklist cramfs
blacklist firewire-core
EOF
Execution Command
Verify that direct or automated requests cannot load the disabled module:
sudo modprobe -v dccp
Realistic Terminal Output
install /bin/true
Line-by-Line Technical Analysis
install /bin/true:modprobeevaluated/etc/modprobe.d/cis-hardening.confprior to resolving dependencies. Finding theinstalloverride, it executed/bin/trueinstead of inserting code into the kernel.- The command exits with status code
0, preventing error cascades in calling programs while ensuring no driver code enters kernel memory.
State Check & Verification
lsmod | grep dccp
echo $?
1
grep -E "dccp|sctp" /proc/modules
(No output returned, confirming the protocol remains absent from live kernel memory)
What the Administrator Does Next
Ensure the hardening rules are baked into the initial ramdisk so they take effect before the root filesystem is mounted:
# On Debian / Ubuntu systems:
sudo update-initramfs -u -k all

# On RHEL / Rocky Linux systems:
sudo dracut -f --regenerate-all
3. Storage Controller & Cryptographic Acceleration Tuning
The Scenario
A high-concurrency database server with encrypted NVMe storage (dm-crypt) is experiencing CPU bottlenecks during bulk data ingestion. The database architect must ensure that hardware-accelerated AES instructions (aesni_intel) are active and that native NVMe multipathing (nvme_core.multipath=Y) is enabled to distribute I/O across redundant PCIe storage paths.
Configuration File
sudo tee /etc/modprobe.d/nvme-crypto.conf << 'EOF'
# Enable native hardware multipath for NVMe subsystems
options nvme_core multipath=Y
# Optimize dm-crypt performance for modern multi-core NVMe arrays
options dm_crypt max_read_size=2097152 max_write_size=2097152
EOF
Execution Command
Load the hardware cryptographic acceleration and storage drivers:
sudo modprobe -v aesni_intel
sudo modprobe -v dm_crypt
sudo modprobe -v nvme_core
Realistic Terminal Output
insmod /lib/modules/6.8.0-40-generic/kernel/arch/x86/crypto/crypto_simd.ko.zst
insmod /lib/modules/6.8.0-40-generic/kernel/arch/x86/crypto/cryptd.ko.zst
insmod /lib/modules/6.8.0-40-generic/kernel/arch/x86/crypto/aesni-intel.ko.zst
insmod /lib/modules/6.8.0-40-generic/kernel/drivers/md/dm-crypt.ko.zst max_read_size=2097152 max_write_size=2097152
Line-by-Line Technical Analysis
insmod .../crypto_simd.ko.zst:modprobedetected thataesni-intelrequires SIMD vector management and loaded the prerequisite module first.insmod .../cryptd.ko.zst: Inserted the asynchronous cryptographic daemon interface.insmod .../aesni-intel.ko.zst: Linked Intel Advanced Encryption Standard New Instructions (AES-NI) directly to the kernel crypto engine.insmod .../dm-crypt.ko.zst max_read_size=...: Applied 2MB chunk sizes directly to the disk encryption target to minimize block fragmentation across NVMe storage queues.
Verification of Multipath and Crypto Acceleration
cat /sys/module/nvme_core/parameters/multipath
grep -A 4 "aesni" /proc/crypto | head -n 5
Y
name         : aes
driver       : aes-aesni-intel
module       : aesni_intel
priority     : 300
refcnt       : 4
What the Administrator Does Next
Verify that NVMe namespaces are actively discovering multiple redundant controllers across the PCIe fabric:
sudo nvme list-subsys
4. Safely Unloading and Reloading Drivers During Live Upgrades
The Scenario
During live hypervisor maintenance, a critical security vulnerability requires upgrading the Mellanox network driver (mlx5_core). The server cannot be rebooted because it is hosting live virtual workloads. The administrator must identify active module locks, safely take down dependent network interfaces, unload the driver tree using modprobe -r, and hot-reload the patched version.
Initial Diagnostic State Check
Inspect current module reference counts and dependencies:
lsmod | grep mlx5
mlx5_ib               421888  0
mlx5_core            2129920  1 mlx5_ib
psample                20480  1 mlx5_core
devlink               225280  2 mlx5_ib,mlx5_core
Attempting Naive Removal
sudo modprobe -rv mlx5_core
modprobe: FATAL: Module mlx5_core is in use.
Resolution Workflow
The output shows that mlx5_ib (InfiniBand subsystem) holds a reference lock on mlx5_core. Additionally, active network interfaces prevent unloading.
# 1. Bring down operational network interfaces bound to the hardware
sudo ip link set dev ens2f0 down
sudo ip link set dev ens2f1 down

# 2. Safely unload the dependency chain in reverse order
sudo modprobe -rv mlx5_ib mlx5_core
Realistic Terminal Output
rmmod mlx5_ib
rmmod mlx5_core
Line-by-Line Technical Analysis
rmmod mlx5_ib: Becausemlx5_ibwas explicitly included in the removal command and had zero active callers once interfaces were down,modprobe -runloaded it first usingdelete_module(2).rmmod mlx5_core: With its dependent module removed,mlx5_core's reference counter reached zero, permitting the kernel to release its memory allocations and cleanly unregister hardware devices.
Reloading the Patched Driver
Rebuild the module index and reload the driver:
sudo depmod -a
sudo modprobe -v mlx5_core
insmod /lib/modules/6.8.0-40-generic/updates/drivers/net/ethernet/mellanox/mlx5/core/mlx5_core.ko.zst
What the Administrator Does Next
Verify that network interfaces have re-initialized properly and bring them back online:
sudo dmesg | grep -E "mlx5_core.*Link is Up"
sudo ip link set dev ens2f0 up
sudo ip link set dev ens2f1 up
5. Automating Container & Virtualization Host Driver Provisioning
The Scenario
An automated deployment script is bootstrapping a bare-metal Kubernetes node running containerd while supporting nested virtual machines. The node requires immediate activation of overlay filesystems (overlay), bridge netfilter packet inspection (br_netfilter), and nested hardware virtualization (kvm_intel nested=1).
Configuration File
Establish persistent parameter overrides and automated boot-time loading:
# Define runtime parameters for nested virtualization
sudo tee /etc/modprobe.d/kvm-nested.conf << 'EOF'
options kvm_intel nested=1 enable_shadow_vmcs=1 enable_apicv=1
EOF

# Define modules to be loaded automatically at system boot
sudo tee /etc/modules-load.d/k8s-virt.conf << 'EOF'
overlay
br_netfilter
kvm
kvm_intel
EOF
Execution Command
Re-index the driver cache and load the stack:
sudo depmod -a
sudo modprobe -v overlay
sudo modprobe -v br_netfilter
sudo modprobe -v kvm_intel
Realistic Terminal Output
insmod /lib/modules/6.8.0-40-generic/kernel/fs/overlayfs/overlay.ko.zst
insmod /lib/modules/6.8.0-40-generic/kernel/net/bridge/br_netfilter.ko.zst
insmod /lib/modules/6.8.0-40-generic/kernel/arch/x86/kvm/kvm.ko.zst
insmod /lib/modules/6.8.0-40-generic/kernel/arch/x86/kvm/kvm-intel.ko.zst nested=1 enable_shadow_vmcs=1 enable_apicv=1
Line-by-Line Technical Analysis
insmod .../overlay.ko.zst: Initializes the union filesystem driver required for container image layering.insmod .../br_netfilter.ko.zst: Enables packet filtering across network bridges, allowing Kubernetes network plugins to manage pod firewall rules.insmod .../kvm.ko.zst: Loads the core hypervisor subsystem.insmod .../kvm-intel.ko.zst nested=1 ...: Initializes Intel virtualization extensions while enabling nested guest hypervisors (nested=1) and interrupt virtualization (enable_apicv=1).
Verification of Runtime Capability
cat /sys/module/kvm_intel/parameters/nested
sysctl net.bridge.bridge-nf-call-iptables
Y
net.bridge.bridge-nf-call-iptables = 1
What the Administrator Does Next
Restart the container and node management daemons to confirm cluster readiness:
sudo systemctl restart containerd
sudo systemctl restart kubelet
What Can Go Wrong: Operational Traps and Diagnostic Recovery
Directly manipulating kernel drivers carries inherent operational risks. An incorrect parameter or an unsafe driver removal can disrupt active services or induce a kernel panic.
| Failure Mode | Observable Symptom | Root Cause | Engineering Solution |
|---|---|---|---|
| 1. The Incomplete Blacklist Illusion | A blacklisted module loads anyway when an application opens a network socket or interacts with hardware. | The blacklist directive only suppresses loads requested by module name; hardware aliases and kernel request_module() calls still resolve the driver. |
Pair blacklist <module> with install <module> /bin/true to redirect all load attempts to a harmless shell stub. |
| 2. The Initramfs Desynchronization Trap | Custom /etc/modprobe.d/ parameters are ignored when the operating system boots up. |
Early boot drivers for storage and networking are loaded from the Initial RAM Disk (initramfs) before the root disk is mounted. |
Rebuild the system ramdisk using update-initramfs -u or dracut -f after modifying boot-critical driver rules. |
3. Dependency & Reference Locks (EBUSY) |
modprobe -r aborts with FATAL: Module is in use. |
Active consumer modules, mounted filesystems, or open network interfaces hold positive reference counts. | Trace dependent modules using lsmod, take down bound network links, and remove modules in reverse topological order. |
1. The Incomplete Blacklist Illusion
The Trap: An administrator places blacklist nouveau inside /etc/modprobe.d/blacklist.conf to prepare a workstation for proprietary GPU drivers. Upon reboot, the open-source driver loads anyway, conflicting with the new software installation.
The Mechanism: The blacklist keyword only prevents modprobe from loading a module based on its exact name. If an internal kernel subsystem or hardware manager requests the driver via a hardware alias (such as a PCI vendor identifier), modprobe fulfills the alias request.
The Fix: Always pair blacklist with an install override directed to a null stub:
sudo tee /etc/modprobe.d/disable-nouveau.conf << 'EOF'
blacklist nouveau
install nouveau /bin/true
EOF
2. The Initramfs Desynchronization Trap
The Trap: An engineer tunes storage driver options in /etc/modprobe.d/nvme.conf, but the machine ignores the new settings following a reboot.
The Mechanism: Boot-critical storage controllers, basic filesystems, and essential networking drivers are loaded during early startup from the Initial RAM Disk (initramfs), long before /etc/modprobe.d/ is accessible on the root drive. If the ramdisk is not refreshed, the system continues running the older configuration embedded inside the archive.
The Fix: Regenerate the ramdisk after changing options for boot-critical hardware:
# On Debian / Ubuntu:
sudo update-initramfs -u -k $(uname -r)

# On RHEL / AlmaLinux / Rocky Linux:
sudo dracut -f /boot/initramfs-$(uname -r).img $(uname -r)
3. Dry-Run Validation to Protect Live Systems
Before applying unfamiliar parameter values or unloading modules on live servers, use dry-run (-n) and verbose (-v) flags together to verify the execution plan:
sudo modprobe -nv bonding
insmod /lib/modules/6.8.0-40-generic/kernel/drivers/net/bonding/bonding.ko.zst mode=802.3ad miimon=100 xmit_hash_policy=layer2+3 lacp_rate=fast
If a configuration file contains syntax errors or invalid parameters, modprobe catches the issue before making system calls, shielding the running kernel from configuration faults.
For additional documentation on module configuration, dependency indexing, and driver development, consult:
- modprobe(8) Linux Manual Page
- modprobe.d(5) Configuration Manual
- depmod(8) Dependency Indexing Manual
- ArchWiki: Kernel Module Management
- Linux Kernel Module Documentation
Today's Takeaway
Open a terminal on your computer right now and run modprobe -c | grep -E "^(options|install|blacklist)" | head -n 30 to inspect the consolidated runtime rules currently governing your machine's kernel. Then cross-reference those directives with your live hardware state by inspecting /proc/modules and browsing the active parameters inside /sys/module/$(lsmod | awk 'NR==2{print $1}')/parameters/. Understanding how configuration files, the dependency map, and kernel memory fit together turns driver management from unpredictable guesswork into a precise, transparent science.